- Joined
- Sep 25, 2021
- Sythe Gold
- 21
- Messages
- 22
- Age
- 27
Link the current Sythe account: MyPvM
Which violation you are reporting the user for: False advertising of their plugin security, making false statements to clients, staff members and other forum users and putting their clients accounts and data at risk.
Why you think they're violating Sythe rules: The accused user has throughout multiple posts and threads claimed that a plugin in their possession, which is used by their Boosters/Staff to access client accounts, is completely secure and does not in any way allow the booster to access client information such as Login/Password or bankpin: Quoting from thread 4224050:
“Clients do NOT have to share details
Clients do NOT have to share bankpin
No booster/worker has ever access to client details.”

The purpose of this report is to debunk the “blatant lies” used here for false advertising and promoting their server / services, allowing the offender to claim a large market share for their services on the base of false security that they are promising their clients and other bystanders reading their content on the forum.
Given this estimation, I highly doubt that this is the solution the offender’s plugin developer has implemented, and I can, with the confirmation of MyPvM through their chat logs, state that their plugin instead works on simple network requests (may it be REST or WS) between the plugin and a server. As no Blackhat activity is allowed on the forum, no attempts to decompile their plugin has been made. Due to this, I can not confirm whether the account data is being transferred in an encrypted or plain-text state. This however does not make a significant difference, as the client’s data would need to be decrypted prior to sending a login request to Runescape servers either way, and for this the encryption/decryption key must be available on the booster’s pc / within the plugin or one of its installer resources.
Any developer with minimal networking knowledge can easily catch the client data packet on its way from the server, decrypt it using the key they already have locally on their pc (or even skip this step if the data isn’t encrypted) and access the clients data whenever/however they may want.
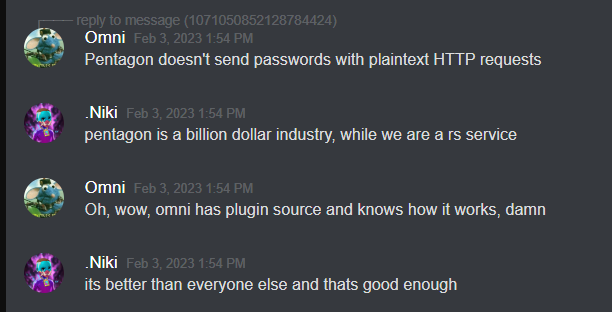
I have made an attempt to inform the offender about this issue privately through their discord ticketing system, and was met with harassment as well as comparing their safety to Pentagon’s security (A system that I am not familiar with, but I must admit to having my doubts) and in the end acknowledgement of them being aware of the security flaw, but as one of the Owners of the server shortly commented, quoting: “So what?”
For the paragraph above, I would like to quote a statement made by the offender in thread 4224050, which contradicts their actions displayed in the transcript: “Nice sources that you have, that can't stand up if it the plugin is so bad that they are jealous of it. @Pikachu please reach out to me (Niki) and I can show you around. There is legit nothing that we hide from public as it is not needed. If anyone else wants to see the amazing way of protecting customer accounts, I will make some time for you. Even though testing > theory. ”

This again proves that when approached about their lies in private, the offender does not withstand their word that is publicly given for everyone to see.
I have included the transcript of the ticket conversation mentioned above, where I was promised a public apology on Sythe from the owners when the security flaw has been proven. Sadly, all I got was a permanent ban from the server titling: “wasting time, proving stuff”.

The fully uploaded and formatted transcript can be found here, to not require any downloading from the staff team in the process of viewing evidence: https://i.imgur.com/zY5EKvo.png
If one of the administrators wishes to see a demonstration of how easily the security plugin can be used to retrieve client’s data (without any Blackhat activity involved) I will be more than glad to demonstrate the full process in private.
I have also developed an equivalently secure plugin myself over the last 2 days to allow for non-lying service providers to stand on the same ground as the offender, as long as no lies are used to market the safety or functionality of said software.
I believe this to be at least a temporarily bannable offense from the offender’s side, as it:
They also refrained from correcting this critical misinformation to their clients when informed about it, meaning that unawareness of the issue can no longer be used as an excuse, and ignorance is not a valid exempt from punishment withing Sythe’s TOS.
Which violation you are reporting the user for: False advertising of their plugin security, making false statements to clients, staff members and other forum users and putting their clients accounts and data at risk.
Why you think they're violating Sythe rules: The accused user has throughout multiple posts and threads claimed that a plugin in their possession, which is used by their Boosters/Staff to access client accounts, is completely secure and does not in any way allow the booster to access client information such as Login/Password or bankpin: Quoting from thread 4224050:
“Clients do NOT have to share details
Clients do NOT have to share bankpin
No booster/worker has ever access to client details.”
The purpose of this report is to debunk the “blatant lies” used here for false advertising and promoting their server / services, allowing the offender to claim a large market share for their services on the base of false security that they are promising their clients and other bystanders reading their content on the forum.
- The clients are indeed required to share their details and bankpin – despite this not being done directly to the booster, the client is obviously required to input their account data for the boosters to be able to access it – this should come as no surprise, but these two points are also not the main focus here, what I want to put complete emphasis on is the third listed argument for why they are, quoting: “the safest and that is not subjective, as it is PROVEABLE”:
- “No booster/worker has ever access to client details”. I’ve been working as a software developer for 13 years, throughout various programming languages, companies and systems, anywhere from Freelancing on my own to developing Military Defence Systems used within NATO countries. With the knowledge I have gained throughout these 13 years, as well as an internal discussion with 2 other military grade developers way past my level of knowledge, we could come up with only one solution to make a plugin like this completely safe and without the booster holding onto the client’s account data on their pc, unencrypted, at one time or another during the login process. We estimated the development time of such a system to take multiple weeks of full-time work of an entire, highly advanced, development team.
Given this estimation, I highly doubt that this is the solution the offender’s plugin developer has implemented, and I can, with the confirmation of MyPvM through their chat logs, state that their plugin instead works on simple network requests (may it be REST or WS) between the plugin and a server. As no Blackhat activity is allowed on the forum, no attempts to decompile their plugin has been made. Due to this, I can not confirm whether the account data is being transferred in an encrypted or plain-text state. This however does not make a significant difference, as the client’s data would need to be decrypted prior to sending a login request to Runescape servers either way, and for this the encryption/decryption key must be available on the booster’s pc / within the plugin or one of its installer resources.
Any developer with minimal networking knowledge can easily catch the client data packet on its way from the server, decrypt it using the key they already have locally on their pc (or even skip this step if the data isn’t encrypted) and access the clients data whenever/however they may want.
I have made an attempt to inform the offender about this issue privately through their discord ticketing system, and was met with harassment as well as comparing their safety to Pentagon’s security (A system that I am not familiar with, but I must admit to having my doubts) and in the end acknowledgement of them being aware of the security flaw, but as one of the Owners of the server shortly commented, quoting: “So what?”
For the paragraph above, I would like to quote a statement made by the offender in thread 4224050, which contradicts their actions displayed in the transcript: “Nice sources that you have, that can't stand up if it the plugin is so bad that they are jealous of it. @Pikachu please reach out to me (Niki) and I can show you around. There is legit nothing that we hide from public as it is not needed. If anyone else wants to see the amazing way of protecting customer accounts, I will make some time for you. Even though testing > theory.
”
This again proves that when approached about their lies in private, the offender does not withstand their word that is publicly given for everyone to see.
I have included the transcript of the ticket conversation mentioned above, where I was promised a public apology on Sythe from the owners when the security flaw has been proven. Sadly, all I got was a permanent ban from the server titling: “wasting time, proving stuff”.
The fully uploaded and formatted transcript can be found here, to not require any downloading from the staff team in the process of viewing evidence: https://i.imgur.com/zY5EKvo.png
If one of the administrators wishes to see a demonstration of how easily the security plugin can be used to retrieve client’s data (without any Blackhat activity involved) I will be more than glad to demonstrate the full process in private.
I have also developed an equivalently secure plugin myself over the last 2 days to allow for non-lying service providers to stand on the same ground as the offender, as long as no lies are used to market the safety or functionality of said software.
I believe this to be at least a temporarily bannable offense from the offender’s side, as it:
- Gave their service a false advantage over other services, who did not refrain to lies about the safety of their systems to their clients.
- Put their clients data and accounts at risk, without clarifying that to the client, and even worse giving them an invalid sense of safety when using their services.
- Gave them a backbone for their marketing, and was used as it since the plugin was taken into use.
They also refrained from correcting this critical misinformation to their clients when informed about it, meaning that unawareness of the issue can no longer be used as an excuse, and ignorance is not a valid exempt from punishment withing Sythe’s TOS.
Last edited: