kThisIsCvpv
Newcomer
- Joined
- Jul 3, 2019
- Sythe Gold
- 12
- Messages
- 10

Dear All,You said they can be compromised, that's enough. + plenty of 3rd party users have merged into this thread or posted separate threads where they will gladly demonstrate the insecurities of the plugin. I will gladly do so myself as well, in which case after the successful demonstration from my side I will require a permanent ban for all the parties who claimed otherwise.
Please realize that the reason why this "demonstration" hasn't been done yet is because he hasn't been able to access my system because it's locked behind authentication that he doesn't have.
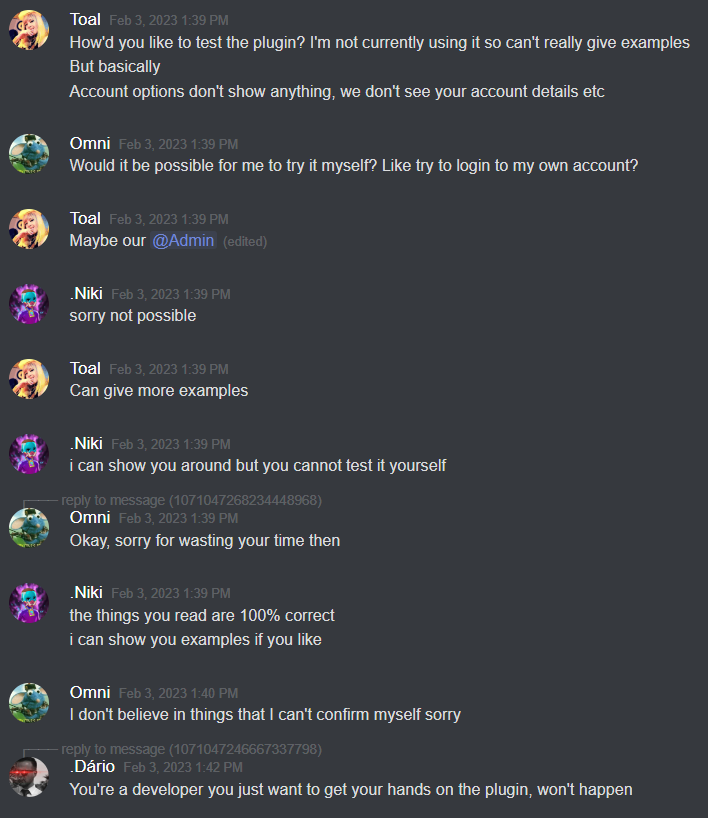
From the uploaded transcript:
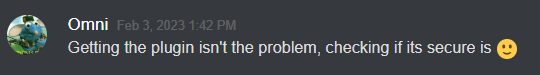
He's able to get my plugin. Don't know how, but sure, whatever.
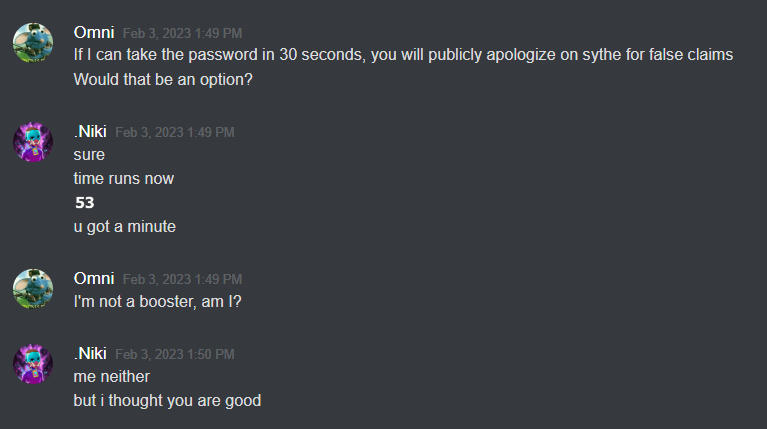
It appears he also knows that you need to be a booster to be able to use the plugin. Therefore, in order to "demo" the plugin's insecurities, he wants me to give him my "keys".
In other words: right now, he doesn't have shit to show. In order to compensate, he proposes a bunch of theoretical situations, hoping one of them will hit the spot.
The equivalent of this is pretty much going to a random Discord server and asking for staff so he can "audit" them.
- Hey @OSRS_Services (sorry to ping you, I don't have anything against you guys, just using this as an example)
- Our discords are getting banned and yours are not!
- This can't be a coincidence!
- Let me go through your emails to see if you're doing anything suspicious!
As someone who's a software developer for 13 years, throughout various programming languages, companies and systems, anywhere from freelancing on their own to developing Military Defence Systems used within NATO countries can't past an authentication panel? Typical. Because the extent of your knowledge only covers HTTPS sniffing, which apperently, you also seem to know very little about. Cry me a river. Anyone can see how delusional and absurd this is.